HackerOne's community-driven Pentest as a Service (PTaaS) uncovers vulnerabilities specific to APIs, leveraging expert methodologies and tailored testing approaches.
CISA 2015 is the backbone of public-private cybersecurity collaboration. As Congress faces reauthorization, here's why letting it lapse would put defenders, and national security, at risk.
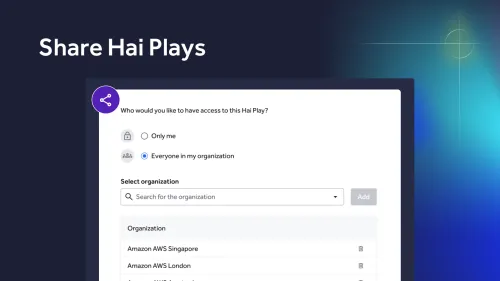
Hai Plays helps security teams move faster, cut repetitive work, and drive consistent results by turning team knowledge into actions across the organization.
CVE-2025-53770 is a critical Microsoft SharePoint vulnerability now under active exploitation. Learn how to respond, assess exposure, and improve visibility with proactive security strategies.
We built a Hai-powered automation to flag critical bug bounty reports faster. Learn how it works and how your team can replicate it to speed up response and reduce risk.
As developers turn to AI tools to speed up coding, a new threat is emerging: slopsquatting. Learn how hallucinated package names in AI-generated code open the door to supply chain attacks, and what you can do to stop them.
The EU’s new GPAI Code lays out how to build AI responsibly, with a big focus on transparency, safety, and security. See why red teaming, bug bounties, and disclosure programs are becoming must-haves for AI developers.