The UK’s Cyber Security and Resilience Bill expands NIS obligations, updates incident reporting, and raises expectations for resilience across digital services.
Security leaders forecast 2026 as the year CTEM becomes essential, with AI-driven threats, agentic security, and continuous validation reshaping cyber risk.
A critical CVE-2025-55182 React RCE flaw affects millions of sites. Get impact details, affected versions, indicators of compromise, and urgent remediation steps.
Bug bounties give security researchers a structured way to report vulnerabilities. This guide explains how bug bounty programs work and why organizations use them.
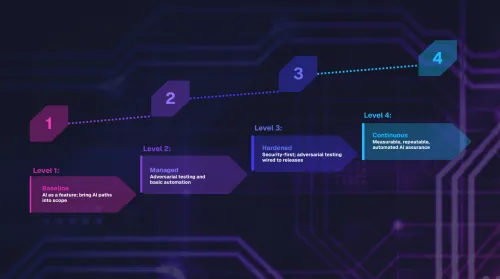
Choose the right AI testing method based on your risk maturity, from add-on LLM pentests to continuous AI assurance. Understand what each level provides.
AI systems demand more than one-off testing. See how to mature from reactive fixes to continuous assurance with layered AI security, safety, and trust practices.